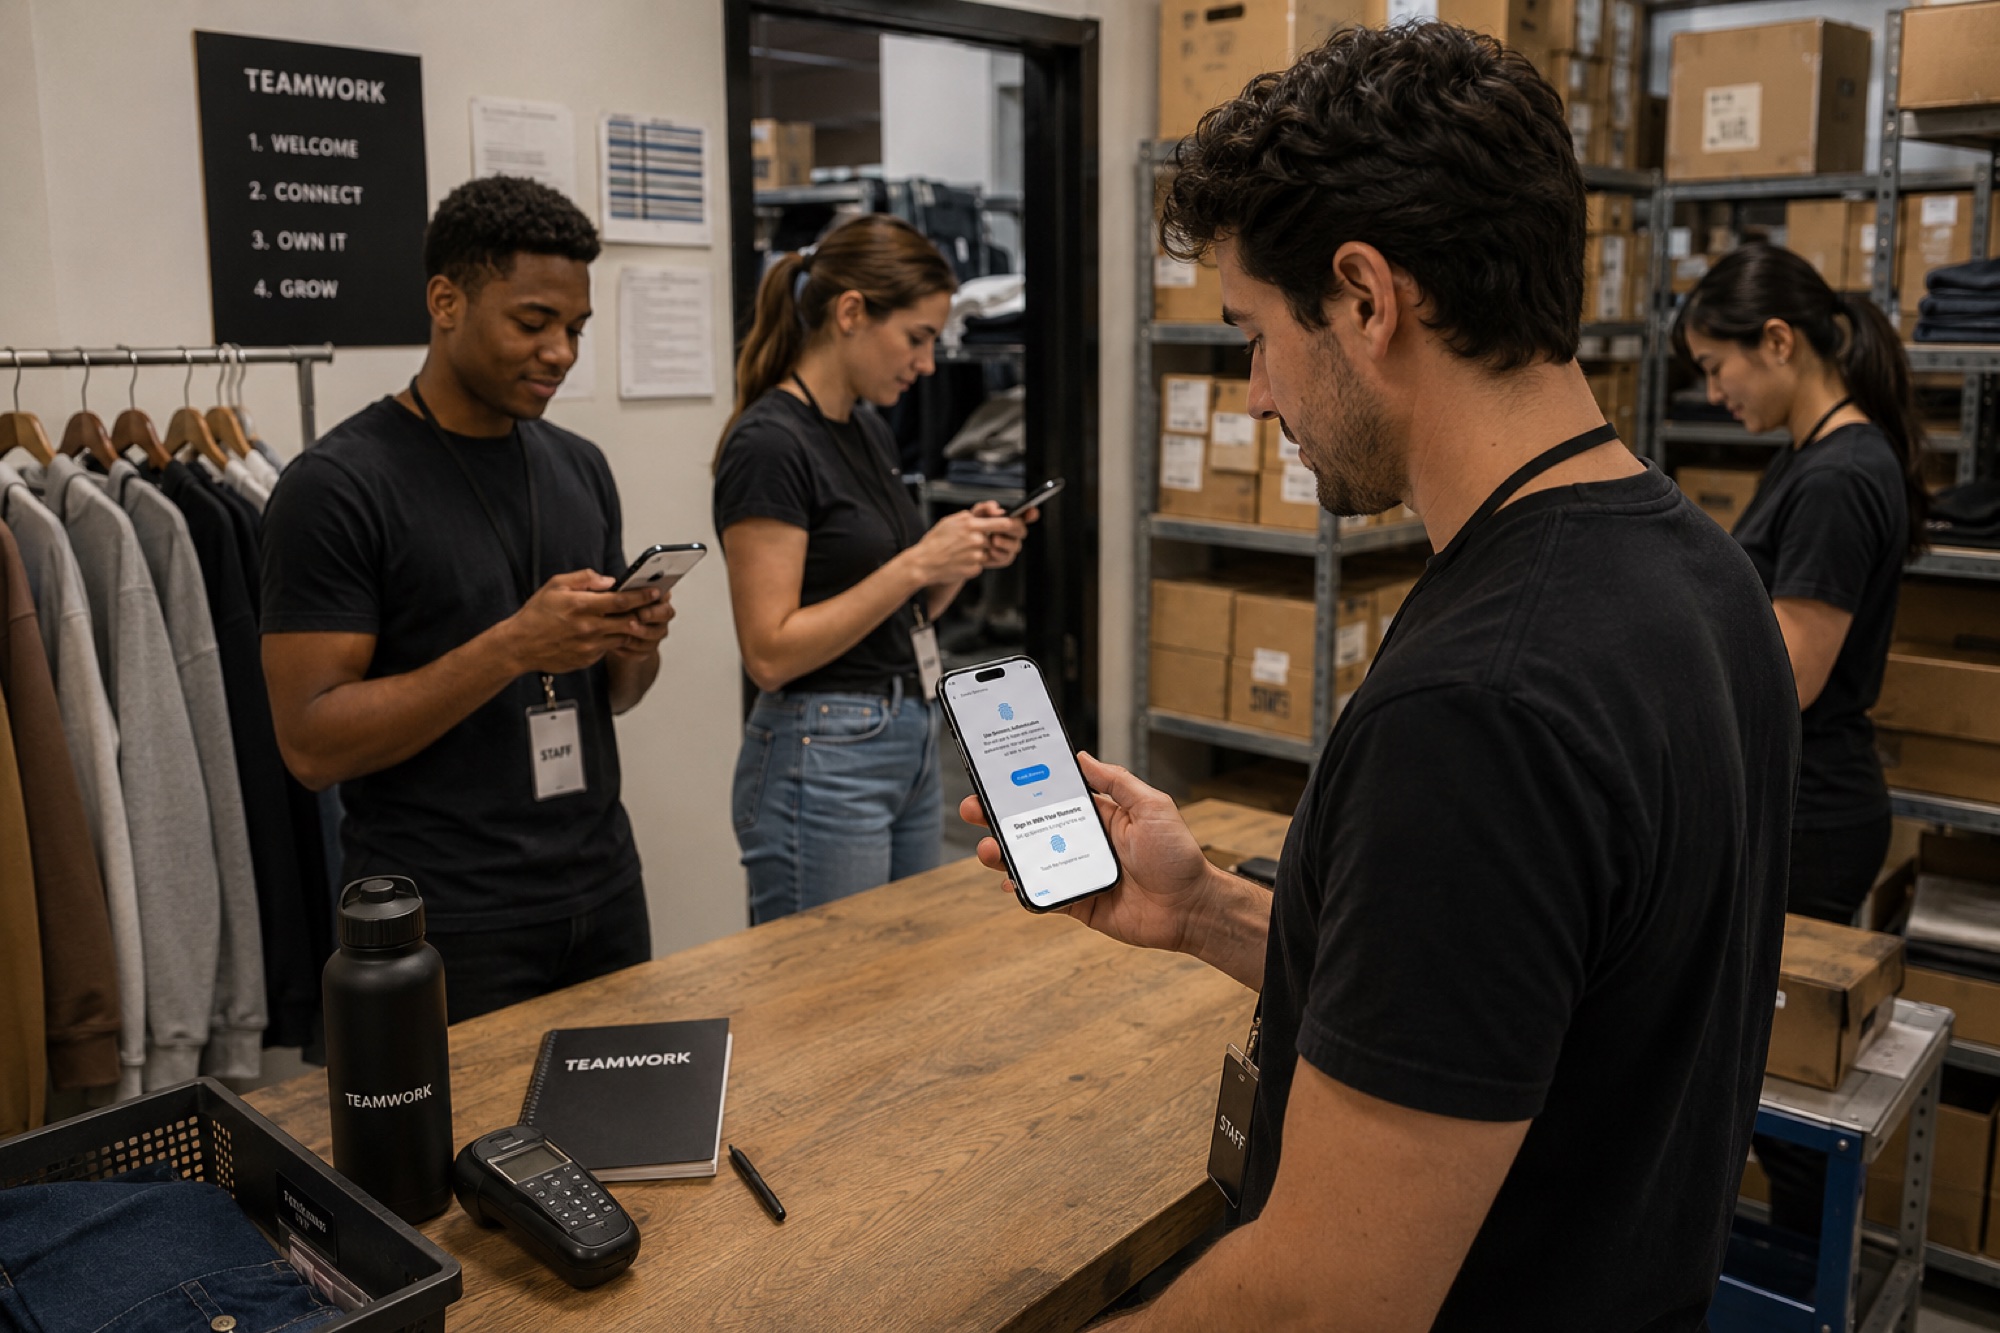
Every associate,
signed in and accountable.
Identity and access management for store systems, on the identity provider you already run. Associates sign in with a rotating QR code, biometrics or a password, and there is no separate user database to maintain.
It is opening time and the network is down. The manager signs in with a password anyway, and the store opens on time.
Permissions as a matrix, not a fixed hierarchy.
Included with every deployment, no add-on required.
Active Directory and SSO integration.
Centralized authentication, user roles and device access, running on the identity provider you already own.
- Integrates with Active Directory and SSO, with MFA handled through your identity provider, so there is no separate user database to maintain
- Associate identities and permissions managed centrally, scoped per role
- Matrixed security rights across hundreds of individual corporate actions, not a handful of coarse presets
- Associates assigned to one location or several, and reassigned whenever you need
- Devices configured centrally in the cloud, so store staff have nothing to set up
- Integrates with HR systems such as Workday
Biometric and rotating QR sign-in.
Secure, rotating QR-code logins for POS terminals and every application. Shared credentials, gone.
- Rotating QR-code authentication, with every sign-in in the audit trail
- Username and password login enforcing character complexity and expiry timelines where you need it
- Every transaction tied to the individual who rang it
- No-sale drawer opens, voids and receipt reprints logged, and exportable to a loss-prevention platform such as Agilence
- Optional multi-user facial recognition on a shared device, identifying individual associates rather than a single enrolled iOS Face ID user
Facial recognition is off by default and enabled at the retailer's discretion, with consent capture and retention periods configured by the retailer and subject to local biometric privacy law. QR-code and credential sign-in give you the same per-associate audit trail without processing biometric data.
Mobile device management
Register and manage company-owned and personal devices side by side, with application access and security policies controlled per device type. Works alongside MDM platforms such as Jamf and AirWatch.
Team member management
Associate records and roles managed in one place, so a new hire is set up once.
What proper identity control changes.
Identity and access questions, answered.
Identity management integrates with Active Directory and SSO, with MFA handled through your identity provider, so authentication continues to run on the identity provider you already own rather than in a separate user database. Device management registers company-owned and personal devices, with application access and security policies controlled per device type, and works alongside MDM platforms such as Jamf and AirWatch.
The retailer chooses. Associates can sign in with a username and password, with complexity and expiry rules where you want them, with a rotating QR code, or with biometrics. Username and password sign-in works offline, so an outage never stops a store from opening.
No. Identity management integrates with Active Directory and SSO, with MFA handled through your identity provider, so authentication runs on the enterprise identity provider you already own. Associate records and roles are managed centrally, so a new hire is set up once.
See it on your own numbers.
Tell us how many stores you run and what you are replacing, and a technical specialist will walk you through the platform against your actual operation, no generic demo.
- A working session, not a slide deck
- Straight to a technical specialist who knows retail
- Your details stay with us, no list sharing
Secure the floor without slowing it down.
See how rotating QR logins, biometric sign-in and matrixed permissions work together.